Expected Behaviour:
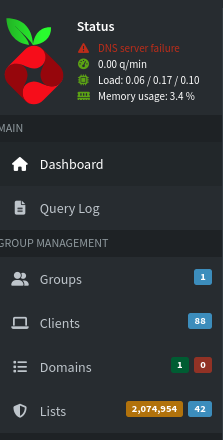
DNS Server is active and blocking queries:
- Raspberry Pi OS
- Raspberry Pi 4
Actual Behaviour:
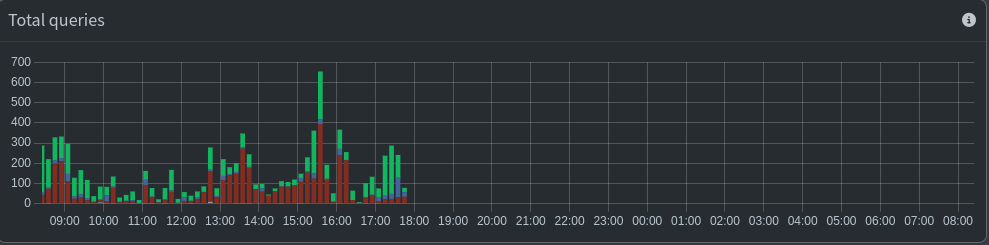
After updating, my Pi-hole no longer is receiving queries. The admin page shows the following:
I did not notice until this morning that I was having this issue:
I have verified that dnsmasq is not running

I have internet and can browse normally, it just appears that my ad blocking is broken at the moment.
Debug Token:
https://tricorder.pi-hole.net/aQqWuVEi/
in my experience when the admin UI looks fine but query count is dead after an update, the hole itself is usually still up and the clients just stopped asking it. since you can browse, something else is answering DNS (router, isp, or a leftover stub).
quick checks id do:
- on a client:
nslookup flurry.com (or whatever) and see which server answers
- in Pi-hole Settings > DNS, confirm its listening on the right interface / "allow only local" vs all, and that the pi's IP didnt change
pihole status and pihole-FTL -vv from ssh, just to see if FTL is actually bound
debug token is already there so the mods can peek, but that client DNS check is usually what tells you if its a "pihole broke" vs "nothing is pointing at it anymore" thing. shrug
Your debug log shows an issue with your settings and this is probably causing the DNS failure.
You added 2 dnsmasq settings:
     dnsmasq_lines = [
       "enable-tftp",
       "tftp-root=/srv/tftp"
     ] ### CHANGED, default = []
But port 69 (TFTP port) is already in use:
*** [ DIAGNOSING ]: Ports in use
    ...
    udp:0.0.0.0:69 is in use by in.tftpd
    ...
    udp:*:69 is in use by in.tftpd
    ...
This is causing a dnsmasq failure:
   2026-09-02 13:07:03.374 BST [6914M] INFO: PID of FTL process: 6914
   2026-09-02 13:07:03.376 BST [6914M] CRIT: Error in dnsmasq configuration: failed to create listening socket for port 69: Address in use
After that, the debug log doesn't show the expected messages related to DNS start.
Suggestion:
As a test, disable in.tftpd or remove the misc.dnsmasq_lines.
If Pi-hole starts after that, the issue is related to the port conflict.
Removed those lines from my config and it immediately started working, thank you!